viewneo is a cloud-based digital signage platform operated by Adversign Media GmbH, a German company certified to ISO/IEC 27001:2022. This page consolidates the security and data-privacy facts that IT managers, security evaluators, and procurement teams in finance, insurance, healthcare, and the public sector need to complete a vendor assessment.
Compliance at a glance
| Topic | Detail |
|---|---|
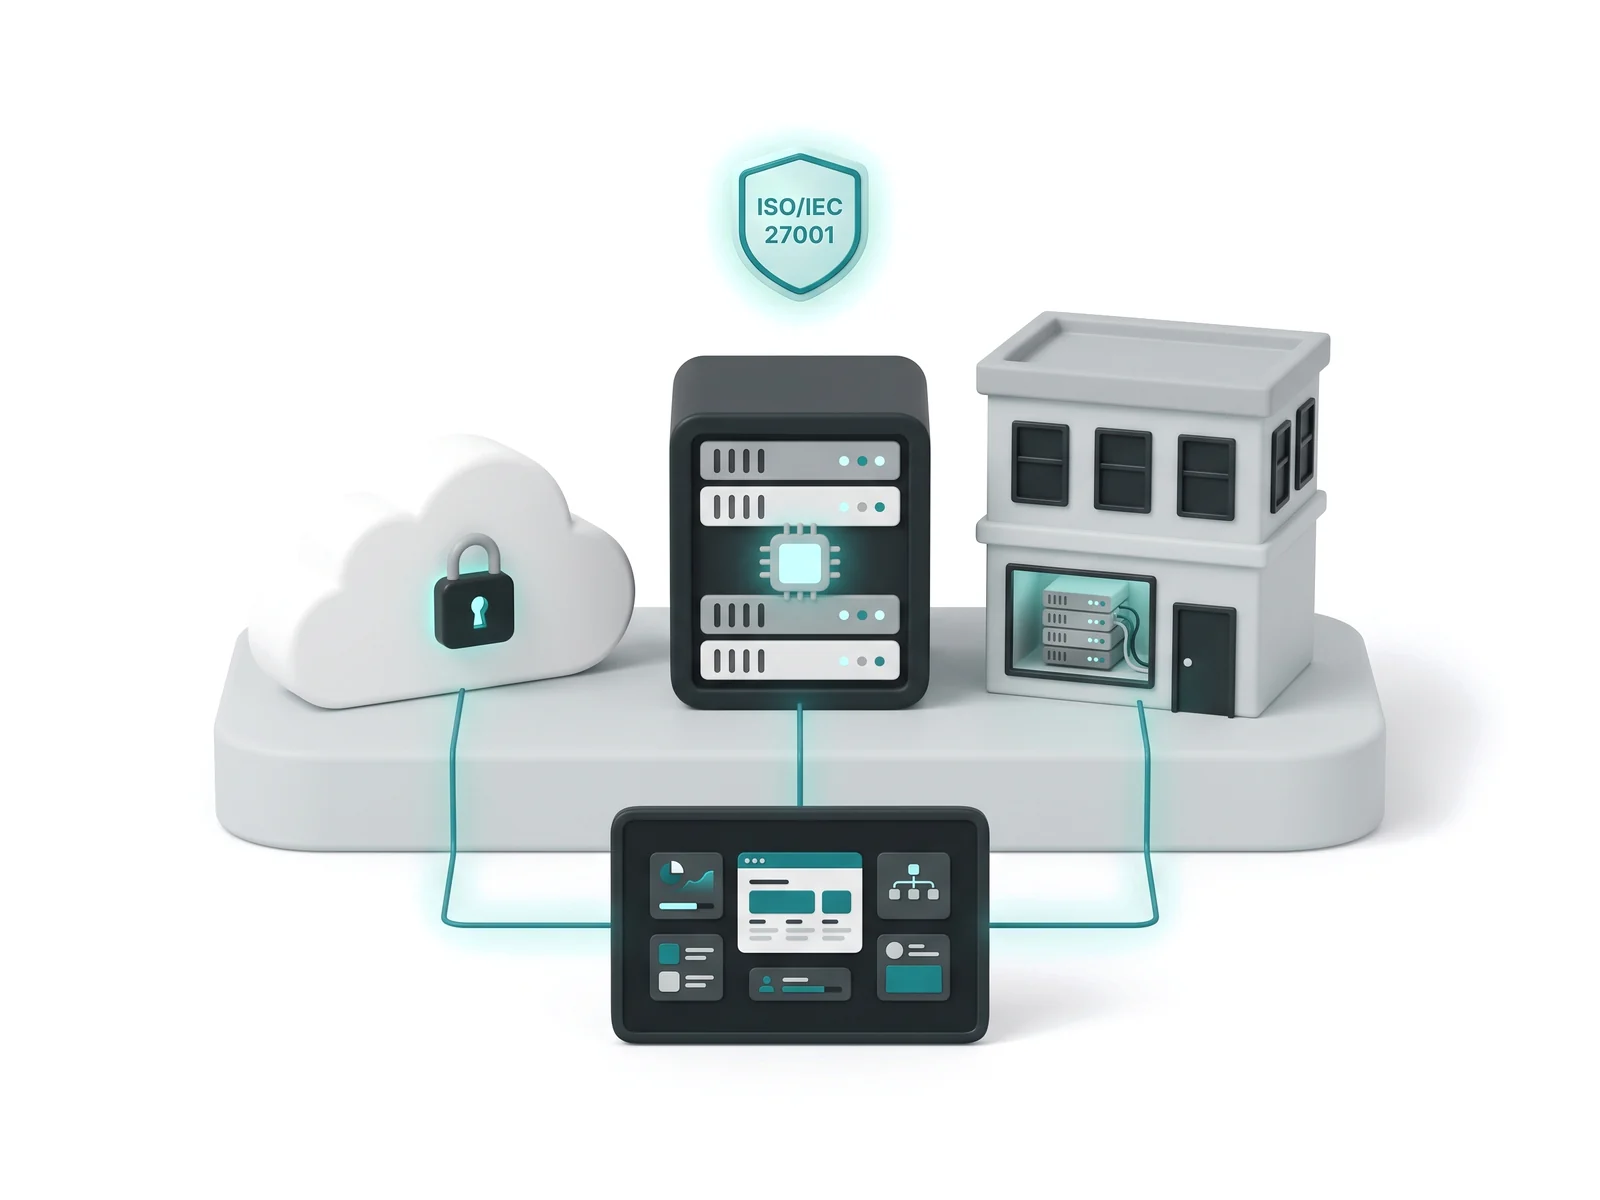
| ISO 27001 | Adversign Media GmbH holds certification to ISO/IEC 27001:2022 — the current version of the international information-security management standard. Our ISMS was assessed by an independent auditor. The certification covers the systems and processes behind the viewneo platform. |
| Data hosting | All viewneo cloud data is hosted on Amazon Web Services (AWS) in Germany (Frankfurt region). Adversign Media GmbH is the data controller. AWS operates as a processor under a formal data-processing agreement (DPA). For organisations that require data to remain entirely on their own infrastructure, viewneo also supports on-premise deployment. |
| GDPR compliance | viewneo is operated from within the EU and processes personal data under GDPR (Regulation (EU) 2016/679). For any data transfers that involve US-based AWS services, two legal mechanisms are in place: EU Standard Contractual Clauses (SCCs) and the EU-US Data Privacy Framework (DPF). Adversign Media GmbH signs data-processing agreements with customers who request them. Full processing details — legal bases, sub-processors, data-subject rights, and retention periods — are set out in the privacy policy. |
What does the public website collect?
The viewneo.com website uses a privacy-friendly, cookieless first-party measurement that records aggregate traffic only — no personal data is stored, no cookies or device identifiers are used, and the measurement runs only when visitors accept it in the “Privacy settings” notice. The site runs no advertising, no cross-site tracking, and no non-essential cookies. Web fonts are self-hosted from the local server — there are no Google Fonts or other third-party CDN requests that could transfer visitor IP addresses to external processors. This design reflects the requirements of GDPR, the German TDDDG, and German case law (LG München 2022 on embedded Google Fonts). See the privacy policy for full details on how this measurement works.
Who controls access inside viewneo Enterprise?
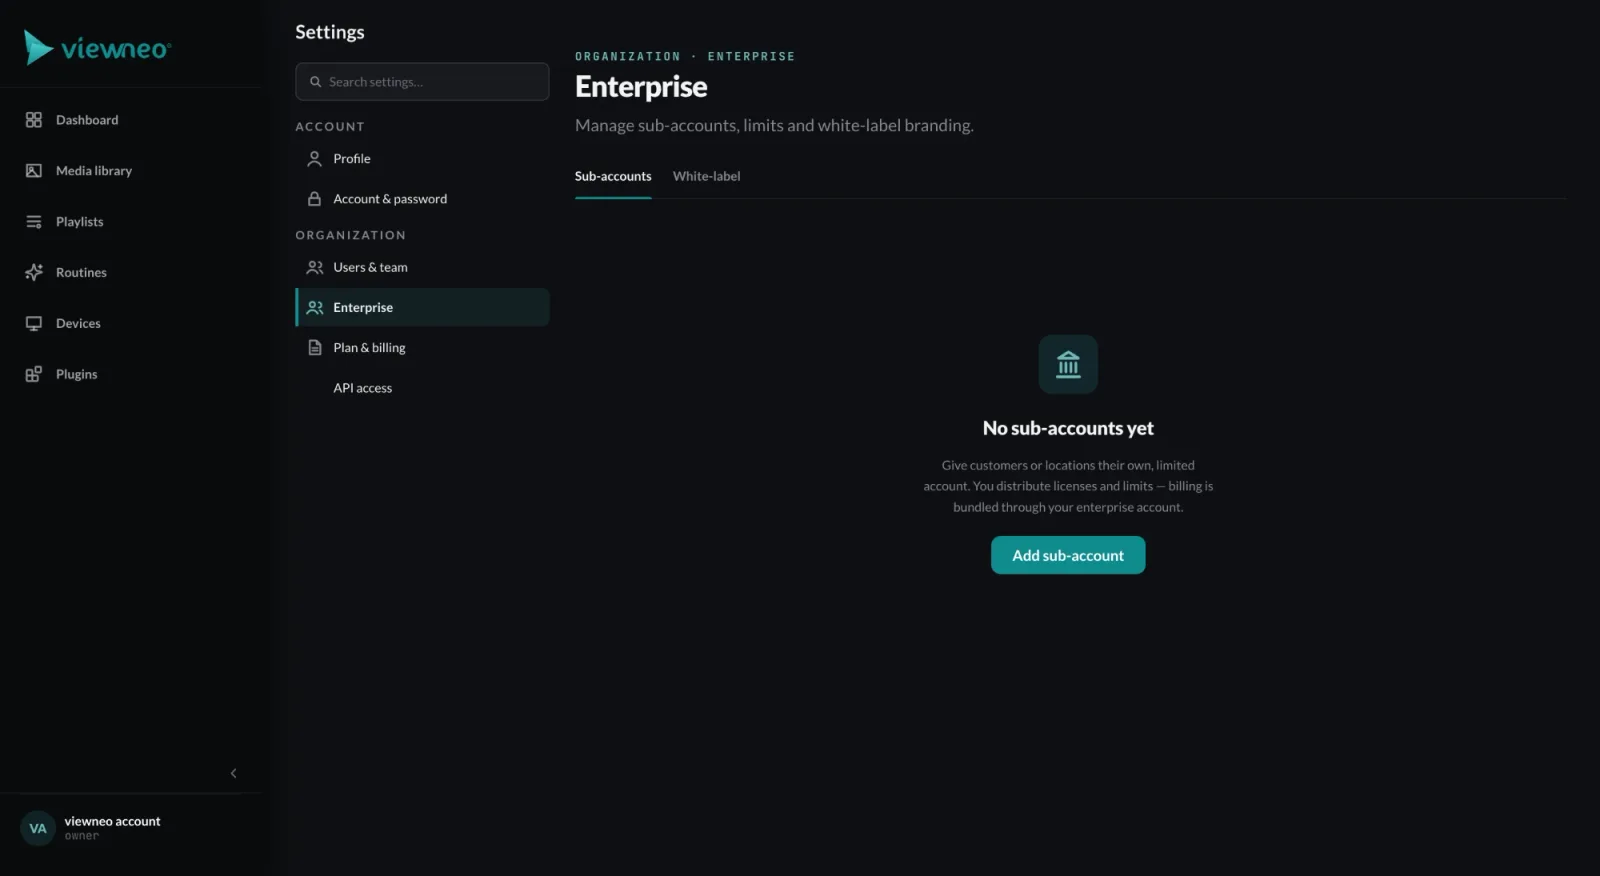
viewneo Enterprise provides role-based access control (RBAC) at two levels: per-account isolation and per-screen permission assignment. Administrators determine which users can manage which screens or groups of screens. Every administrative action is recorded in an audit log, giving security teams a clear trail for incident response, access reviews, and compliance audits.
What are the deployment options for strict data-governance environments?
Organisations in regulated industries — banking, insurance, healthcare, public sector — that cannot route operational data through external cloud infrastructure can deploy viewneo on-premise. An on-premise deployment keeps content, device telemetry, and scheduling data within the organisation’s own network perimeter. The cloud and on-premise options are described on the viewneo Enterprise page. To discuss which model fits your governance requirements, contact our sales team.
Get started
Security evaluators and IT procurement teams are welcome to request a technical briefing. Book a demo using the link above, or send your security questionnaire to the contact page. Legal entity details are in the imprint.